


Free shipping

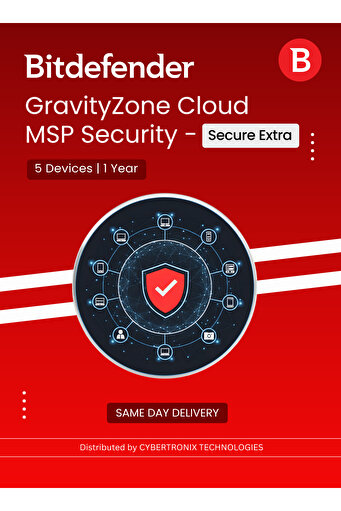
Bitdefender GravityZone Cloud MSP Security - Secure Extra 5 Devices|Digital Lic| SAME DAY DELIVERY
No reviews yet.
4,580
AED
(incl. VAT)
Delivery address
Free shipping
Local delivery
Estimated delivery: 23 - 26 October
Select your address, find out the delivery date!
Trendyol's commitments
Easy and free return in 15 days.
Payment methods

Highlighted features:
BITDEFENDER GravityZone Cloud MSP Security - Secure Extra 5 Devices|Digital Lic| SAME DAY DELIVERY features
Product Type
Not specified
Color
Red
Origin
AE
Cybertronix Technologies
9.7
Seller information
BITDEFENDER GravityZone Cloud MSP Security - Secure Extra 5 Devices|Digital Lic| SAME DAY DELIVERY reviews
No reviews yet.
Product details
Product description
Bitdefender GravityZone Cloud MSP Security – Secure EXTRA (5 Devices) is the most comprehensive managed security tier within the GravityZone MSP portfolio, designed for Managed Service Providers (MSPs) who need advanced, expert‑assisted, cross‑environment threat protection across five endpoints (workstations or servers).
This tier includes all capabilities of the Secure and Secure PLUS levels — such as robust multilayer threat prevention, EDR (Endpoint Detection and Response), and 24×7 Managed Detection and Response (MDR) — and adds Extended Detection and Response (XDR).
XDR correlates and analyzes security telemetry across endpoints, cloud apps, identities, and productivity systems to provide deeper visibility, richer threat context, and cross‑layer detection and response.
Secure EXTRA empowers MSPs to detect, investigate, and respond to sophisticated attacks with both automated analytics and expert guidance from Bitdefender’s security operations teams.
FEATURES * Comprehensive Multilayer Threat Prevention – Uses advanced machine learning, exploit defense, behavioral monitoring, firewall, and network attack defense to block known and unknown threats.
* Advanced Threat Security (ATS) – Tunable machine learning and sandbox analysis provide deep inspection to catch sophisticated malware and zero‑day attacks.
* Endpoint Detection &
Response (EDR) – Detects, investigates, and responds to suspicious endpoint activity with guided workflows.
* 24×7 Managed Detection &
Response (MDR) – Bitdefender SOC analysts provide continuous threat monitoring, expert investigation, and context‑based response support for active incidents.
* Extended Detection &
Response (XDR) – Correlates telemetry from endpoints, identity platforms, cloud services, and productivity applications to reveal complex attack paths and provide richer threat insights.
* Cross‑Layer Threat Correlation – Combines signals from multiple sources to reduce blind spots and support faster, more accurate detection of multi‑stage attacks.
* Identity and Productivity Telemetry Sensors – XDR leverages identity and productivity application signals to detect account‑based threats and lateral movement.
* Human‑Led Threat Hunting – Security analysts proactively seek hidden or stealthy threats that automated systems might miss.
* Context‑Rich Incident Response Guidance – Expert recommendations help MSPs contain and remediate threats efficiently.
* Centralized Cloud‑Based Management Console – MSPs manage all security policies, alerts, and telemetry across all clients and devices from a unified interface.
Additional info
- Sold by .
- A maximum of 5 units of this product can be ordered. Trendyol reserves the right to cancel orders over 5 units.
- Barcode No: 5949958022565
- Origin: AE
BITDEFENDER GravityZone Cloud MSP Security - Secure Extra 5 Devices|Digital Lic| SAME DAY DELIVERY features
Product Type
Not specified
Color
Red
Origin
AE
Safety information
Product safety information